Mini-Module
Summary
The SIEM 101 module provides structured coverage of essential concepts and techniques in SIEM 101. The module covers topics including Alerting, Log Aggregation and Parsing, Log Collection, Log Storage, SIEM Introduction.
Recommended prior knowledge:
- General understanding of cybersecurity concepts
SIEM Introduction
Security information and event management (SIEM) is a security solution that collects and interprets data within the organization and then detects potential threats. Thanks to SIEM, security threats can be monitored in real-time. In this training, we will explain how a SIEM works in general. Without going too deep, we're going to provide you enough information for the SOC analyst to understand what's going on behind the scenes. At the end of the training, you will have a general understanding of the following topics:
How does SIEM work?
How does SIEM collect logs?
Log storage
Creating alerts
SIEM Products
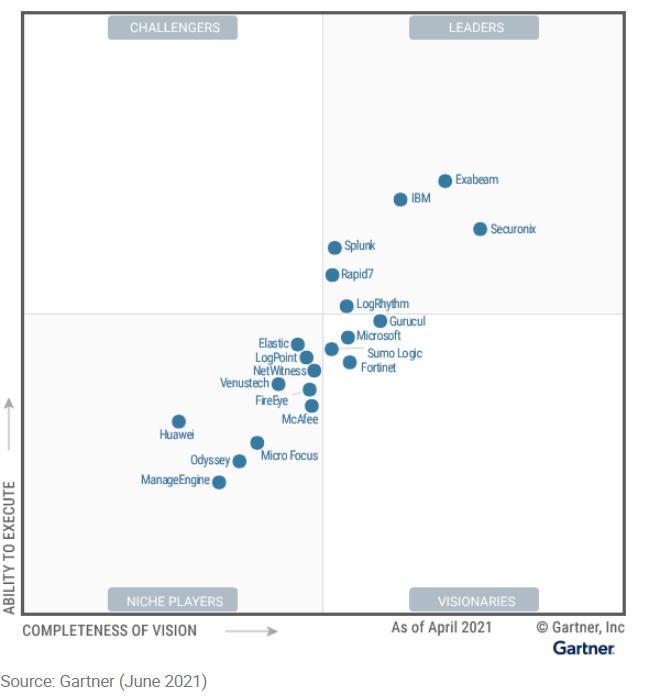
There are many SIEM solutions on the market. According to the Gartner 2021 report, the most successful commercial SIEM solutions are as in the image below.
SIEM and SOC Analyst
Potential threats detected with SIEM are reviewed by SOC analysts. For example, you can think of the alerts on the LetsDefend Monitoring page as alerts created by SIEM.