 Mini-Module
Summary
The AWS S3 Basics module is designed for cybersecurity professionals, Cloud security enthusiasts, IT administrators, and AWS beginners. Throughout this module, students will develop a foundational understanding of AWS S3 basics in the context of cybersecurity, essential best practices for secure data storage within Amazon Simple Storage Service, and acquire practical skills to implement cybersecurity measures for AWS S3 deployments.
Recommended prior knowledge:
- Basic knowledge of cybersecurity concepts
- Familiarity with cloud computing fundamentals
- No prior experience with AWS required, but it's beneficial
Introduction to AWS S3
What is S3?
Amazon Simple Storage Service, commonly known as Amazon S3, is a highly scalable cloud-based storage solution offered by Amazon Web Services (AWS). It is a simple, secure, and fast way to store and retrieve data from anywhere on the web. Whether you are an SMB or an enterprise-level organization, Amazon S3 provides reliable, durable, and cost-effective storage solutions for your organization's needs.
How S3 Works?
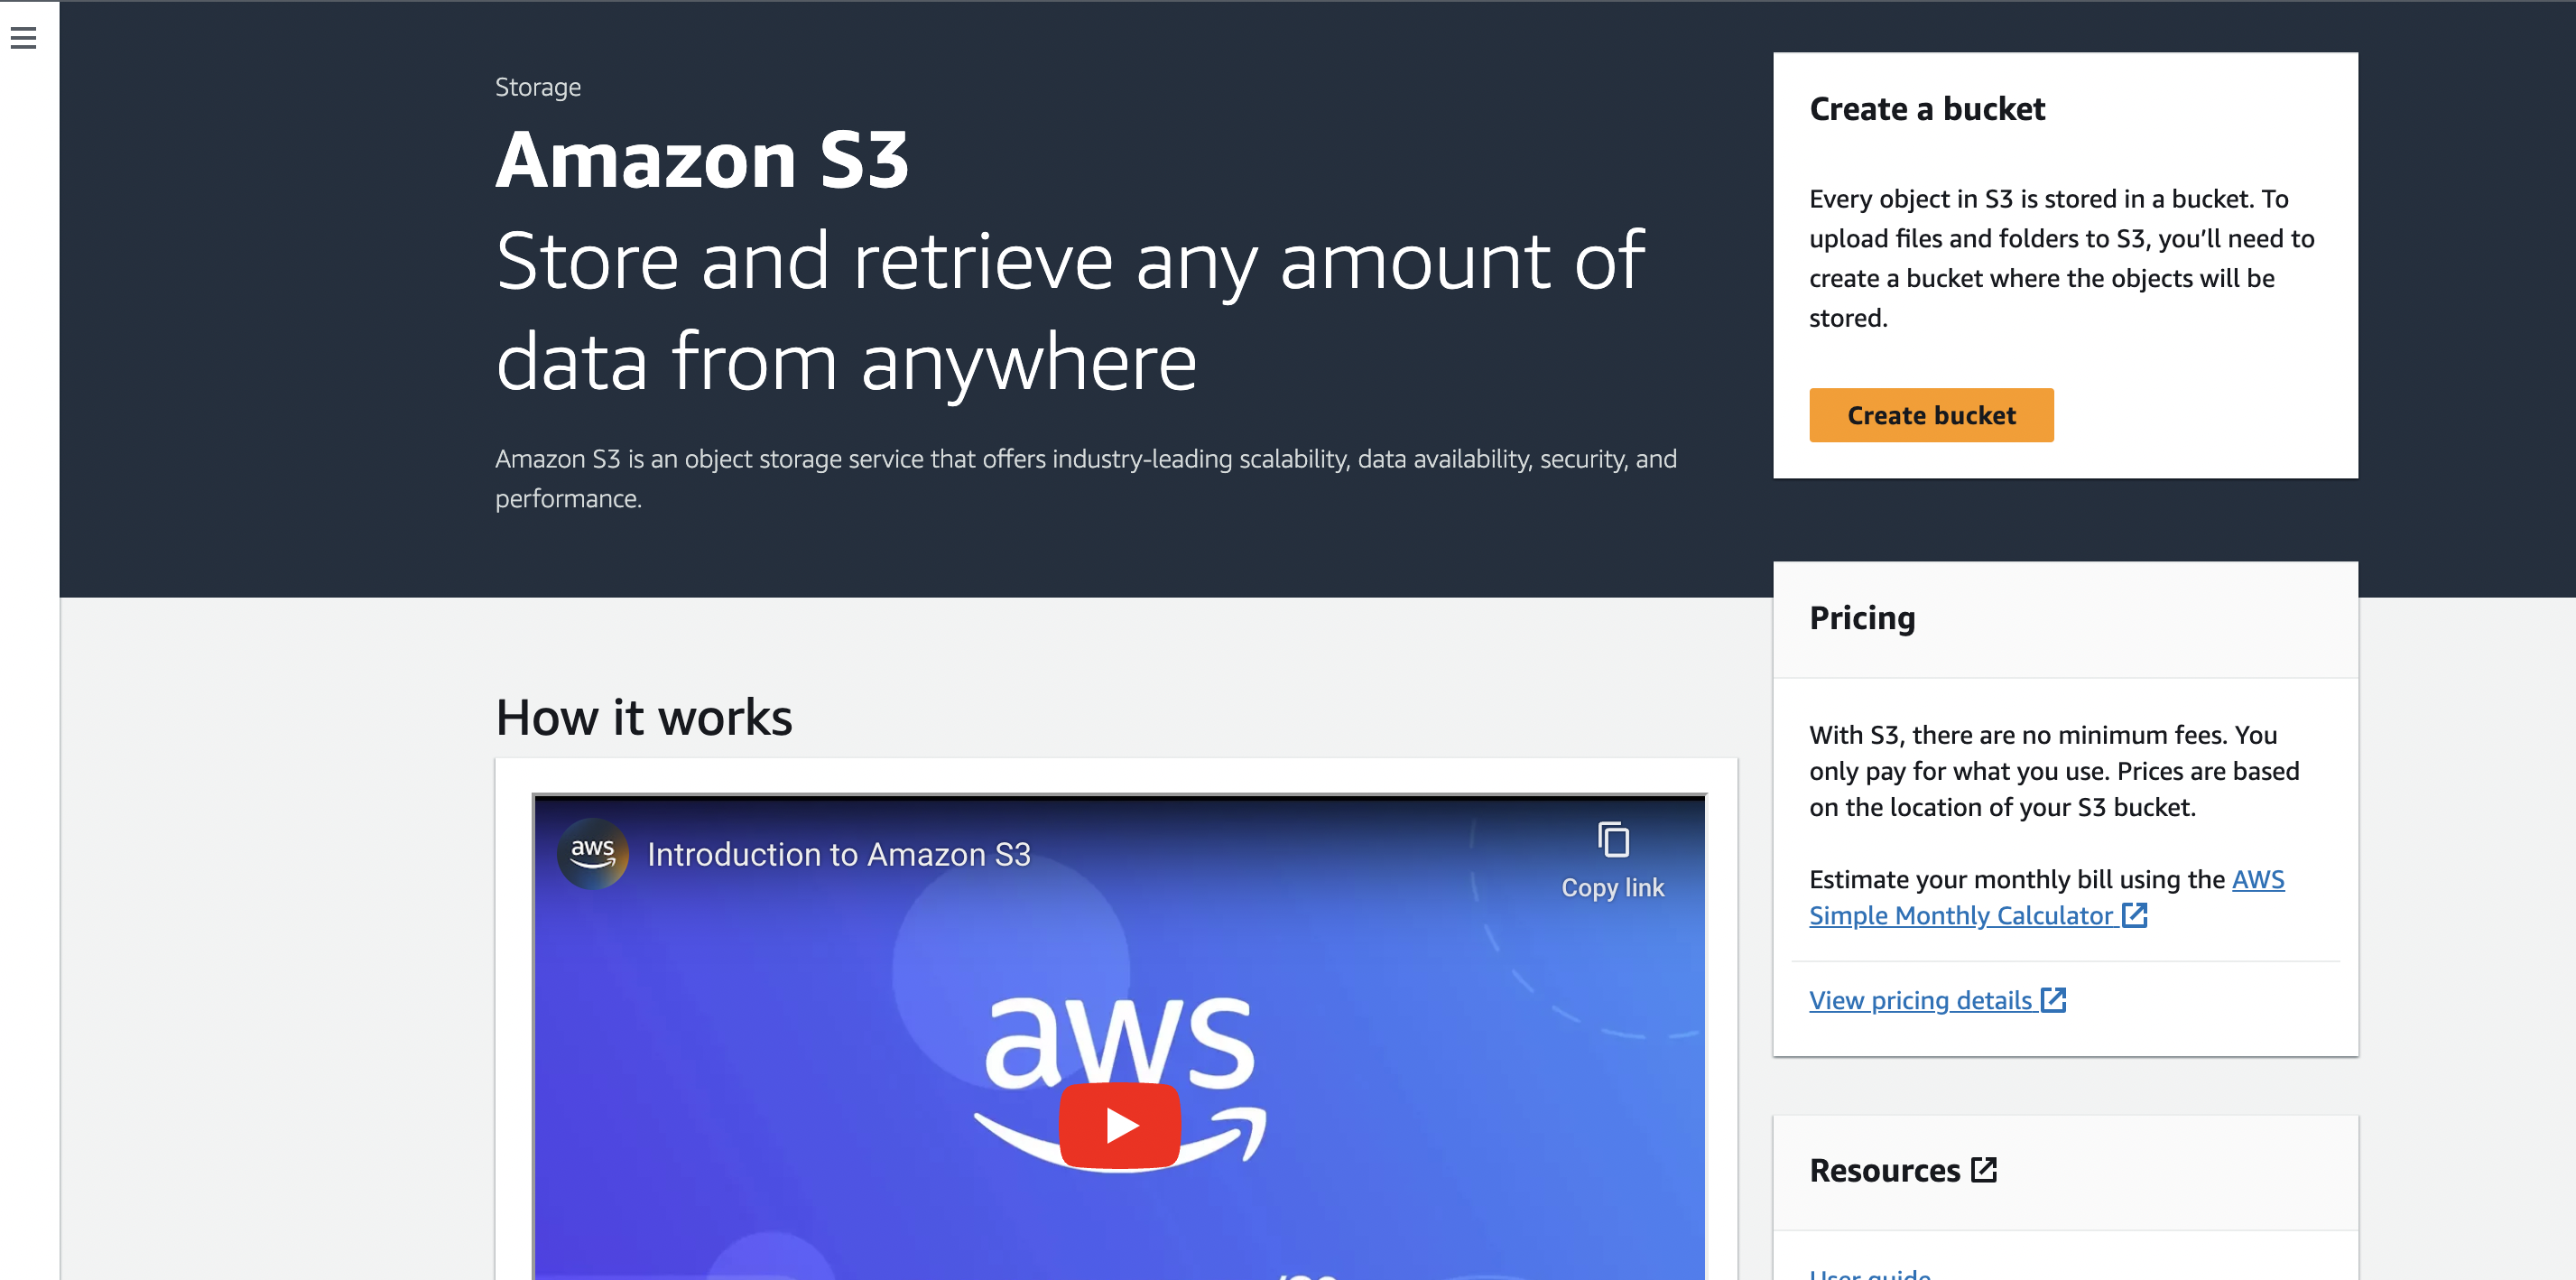
Amazon S3 is a storage service where data is stored as objects within containers called buckets. An object consists of a file and its associated metadata. When using Amazon S3, you begin by creating a bucket and specifying a unique name and region. Then, you can upload your data as objects to that bucket. Each object has a key, which serves as its unique identifier within the bucket.
To cater to different use cases, Amazon S3 offers various configurable features. For instance, you can utilize S3 Versioning to maintain multiple versions of objects within the same bucket, enabling easy restoration of accidentally deleted or overwritten files.
By default, buckets and their objects are private, and access permissions must be explicitly granted. You can manage access through mechanisms such as bucket policies, AWS Identity and Access Management (IAM) policies, access control lists (ACLs), and S3 Access Points. These tools allow you to control who can interact with your buckets and objects.
Key Features and Functionalities of AWS S3
Amazon S3 is a highly flexible and feature-rich service that offers an array of storage options to meet various use cases. Some of its key features and functionalities include:
Scalability: Amazon S3 is highly scalable, allowing you to store as much data as you need. It can store an unlimited number of objects, each up to 5 terabytes in size.
Data protection and security: Amazon S3 offers several mechanisms to protect and secure your data, including data encryption at rest and in transit, granular access controls, and multi-factor authentication.
Durability and availability: Amazon S3 is designed for maximum durability, with 99.999999999% durability, and provides high availability through its global infrastructure.
Cost-effectiveness Amazon S3 offers volume-based pricing options, making it a cost-effective storage solution for organizations of all sizes.
Static Website Hosting: S3 allows users to host static websites directly from their storage buckets, providing a scalable and cost-efficient solution for web hosting.
Data Archiving: The Glacier integration with S3 enables users to archive infrequently accessed data at a lower cost while maintaining the ability to retrieve it when needed.
Data Analytics: S3 is often used as a data lake for analytics, enabling organizations to store vast amounts of data in its native format and analyze it using various AWS analytics services.
Creating and Configuring S3 Buckets
Creating an S3 bucket is a simple process. You can create a new bucket by navigating to the S3 console and selecting the "Create bucket" option. Once you create a bucket, you can configure it based on your requirements. Some of the commonly used S3 configuration options include:
Versioning: You can use versioning to store multiple versions of an object in the same bucket. This is useful when you want to keep track of changes to an object over time.
Logging: S3 provides access logs that provide information on who accessed an object and when.
Lifecycle: You can use lifecycle policies to automate the transition of objects from one storage class to another.
Here is step-by-step guide to create an S3 bucket;
- Log in to your account and navigate to the AWS Management Console, where you'll find the Amazon S3 console.
- Select the Create bucket option.
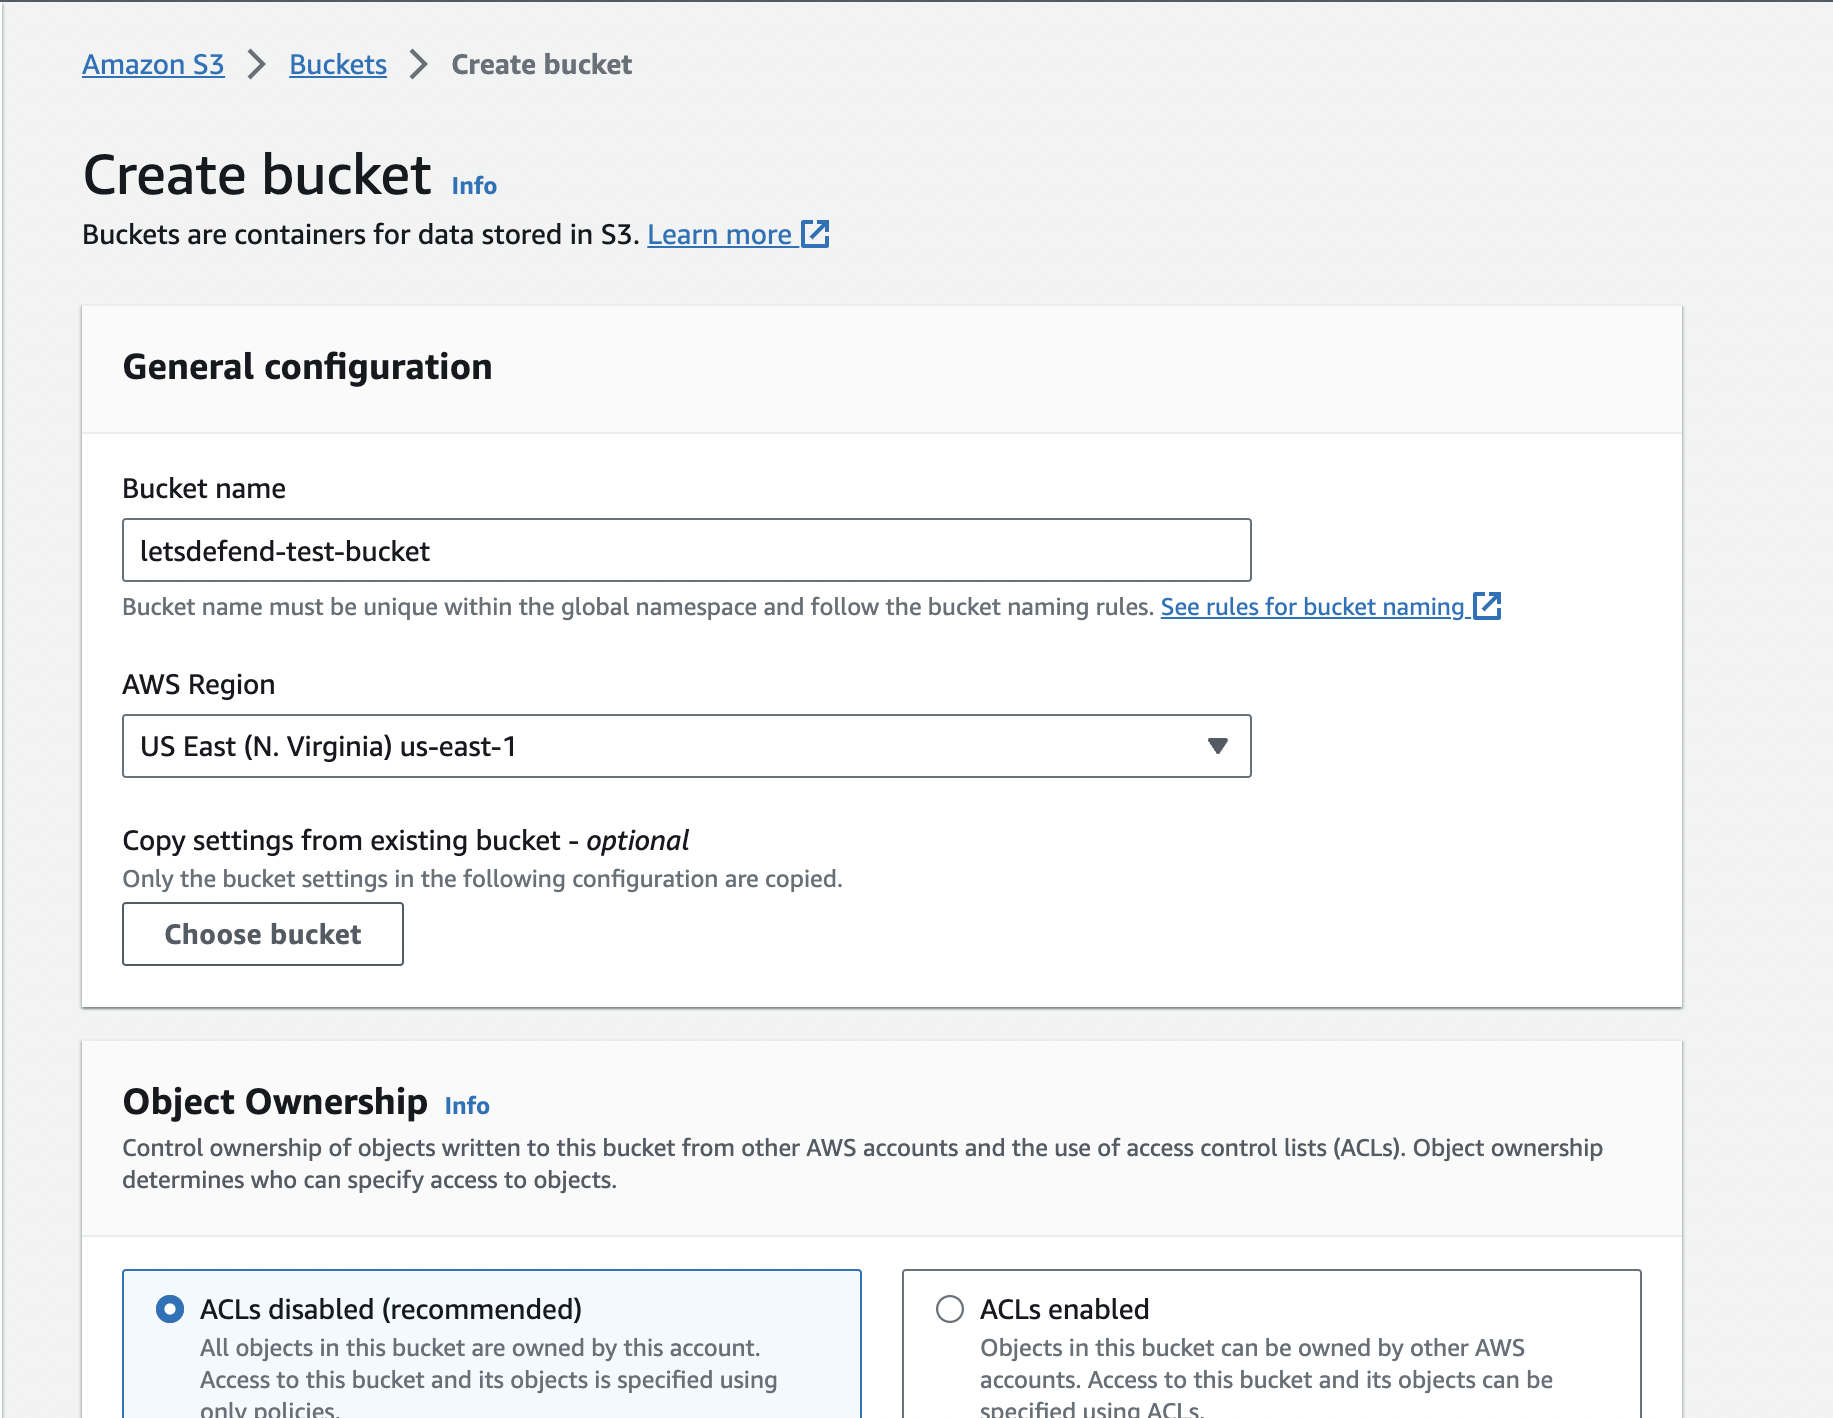
- Choose Object Ownership
- Click Create a bucket
Object Ownership : Amazon S3 Object Ownership is a feature at the bucket level that allows control over object ownership and the enabling or disabling of access control lists (ACLs). By default, Object Ownership is set to "Bucket owner enforced," disabling all ACLs. With ACLs disabled, the bucket owner automatically owns and controls all objects using access-management policies like IAM user policies and S3 bucket policies. It is recommended to keep ACLs disabled, unless specific object-level access control is necessary.
If ACLs are enabled:
Bucket owner preferred : Accepts and honors bucket and object ACLs. Objects with the "bucket-owner-full-control" canned ACL are owned by the bucket owner. Other ACL behaviors remain unchanged. This setting does not affect the ownership of existing objects.
Object writer : Objects are owned by the AWS account that uploads them, even if it's different from the bucket owner's account. Bucket policies can't grant access to objects owned by other AWS accounts. Access permissions for these objects must be managed by the object writer or the bucket owner through object ACLs, but the latter requires prior permissions from the object writer.
S3 Bucket Properties
Understanding S3 bucket properties, such as versioning and logging, is essential for managing and securing your data in Amazon S3. Let's explore each of these properties in detail:
Versioning : Versioning in Amazon S3 allows you to keep multiple versions of an object in the same bucket. When versioning is enabled for a bucket, every update made to an object creates a new version, preserving the previous versions as well. This feature is useful for maintaining a history of changes and recovering from accidental deletions or overwrites.
Enabling versioning for a bucket is simple. You can configure it through the AWS Management Console, AWS CLI, or SDKs. Once enabled, you can view, retrieve, and restore any version of an object stored in your bucket.
Logging : Server access logging in Amazon S3 allows you to capture detailed information about requests made to your bucket. By enabling logging, you can gain insights into who accessed your objects, when the access occurred, and the action performed.
To enable logging, you can use either a bucket policy or bucket access control lists (ACLs). It is recommended to use a bucket policy for granting permissions to Amazon S3 for log delivery. You can configure the log data to be delivered to another bucket or even another AWS account for enhanced security. Once enabled, you can analyze the log data to monitor activity and detect any suspicious behavior.
Permissions : Managing permissions for S3 buckets is crucial for securing your data and controlling access to it. You can define access control through bucket policies and access control lists (ACLs). Bucket policies are the recommended approach for granting permissions in Amazon S3. You can specify who has access to the bucket, what actions they can perform, and under what conditions these permissions apply.
With bucket policies, you can set fine-grained access controls, specify IP restrictions, or even integrate S3 access with AWS Identity and Access Management (IAM). By following the principle of least privilege, you can ensure that only authorized users or applications have access to your S3 data.
By understanding and configuring these S3 bucket properties, you can effectively manage versioning, gain insights into bucket activity through logging, and control access to your data through proper permissions.
Amazon S3 has become a cornerstone in the world of cloud computing, retrieving, and analyzing data at scale with unmatched durability and performance. Its features, coupled with the ability to integrate seamlessly into the broader AWS ecosystem, make it an essential component for building robust and scalable cloud infrastructures. As organizations continue to embrace the cloud, understanding the capabilities and importance of AWS S3 is crucial for optimizing data storage and management strategies.
In the next section, we will discuss the security best practices you need to implement for Amazon S3.